Linux menu

Showing posts with label Ethical Hacker In Linux. Show all posts

Thursday, January 14, 2016

How to Hack Website Using Sql Map in Kali Linux - Sql Injection

How to Hack Website Using Sql Map 


In this tutorial i'm going to explain how to hack a website using sql map,  sqlmap is an open source penetration testing tool that automates the process of detecting and exploiting SQL injection flaws and taking over of database servers. This tool is available in Kali Linux (Hacker's Os).


Let's start with Kali Linux,


Kali Linux


First off, you need to have Kali linux (or backtrack) up and running on your machine. Any other Linux distro might work, but you'll need to install Sqlmap on your own. Now if you don't have Kali Linux installed, you might want to go to this page: An Introduction to Hacker's OS Kali Linux and Installation Tutorial

Suggest you to read: Kali Linux Tutorial: Find Vulnerabilities for Any Website Using Nikto


Sqlmap


Basically its just a tool to make Sql Injection easier. Their official website  introduces the tool as -"sqlmap is an open source penetration testing tool that automates the process of detecting and exploiting SQL injection flaws and taking over of database servers. It comes with a powerful detection engine, many niche features for the ultimate penetration tester and a broad range of switches lasting from database fingerprinting, over data fetching from the database, to accessing the underlying file system and executing commands on the operating system via out-of-band connections."
A lot of features can be found on the SqlMap website, the most important being - "Full support for MySQL, Oracle, PostgreSQL, Microsoft SQL Server, Microsoft Access, IBM DB2, SQLite, Firebird, Sybase and SAP MaxDB database management systems." That's basically all the database management systems. Most of the time you'll never come across anything other than MySql. 

Hacking Websites Using Sqlmap in Kali linux

Sql Version


Boot into your Kali linux machine. Start a terminal, and type -
 sqlmap -h
It lists the basic commands that are supported by SqlMap. To start with, we'll execute a simple command
sqlmap -u <URL to inject>. In our case, it will be-

 sqlmap -u http://testphp.vulnweb.com/listproducts.php?cat=1
Sometimes, using the --time-sec helps to speed up the process, especially when the server responses are slow.
 sqlmap -u http://testphp.vulnweb.com/listproducts.php?cat=1 --time-sec 15
Either ways, when sqlmap is done, it will tell you the Mysql version and some other useful information about the database.


answered in yes/no. Typing y means yes and n means no. Here are a few typical questions you might come across-
  • Some message saying that the database is probably Mysql, so should sqlmap skip all Note: Depending on a lot of factors, sqlmap my sometimes ask you questions which have to be other tests and conduct mysql tests only. Your answer should be yes (y).
  • Some message asking you whether or not to use the payloads for specific versions of Mysql. The answer depends on the situation. If you are unsure, then its usually better to say yes.

Enumeration

Database

In this step, we will obtain database name, column names and other useful data from the database.


So first we will get the names of available databases. For this we will add --dbs to our previous command. The final result will look like -
 sqlmap -u http://testphp.vulnweb.com/listproducts.php?cat=1 --dbs

So the two databases are acuart and information schema.

Table

Now we are obviously interested in acuart database. Information schema can be thought of as a default table which is present on all your targets, and contains information about structure of databases, tables, etc., but not the kind of information we are looking for. It can, however, be useful on a number of occasions. So, now we will specify the database of interest using -D and tell sqlmap to enlist the tables using --tables command. The final sqlmap command will be-
 sqlmap -u http://testphp.vulnweb.com/listproducts.php?cat=1 -D acuart --tables
The result should be something like this - 


Now we have a list of tables. Following the same pattern, we will now get a list of columns.

Columns

Now we will specify the database using -D, the table using -T, and then request the columns using --columns. I hope you guys are starting to get the pattern by now. The most appealing table here is users. It might contain the username and passwords of registered users on the website (hackers always look for sensitive data).
The final command must be something like-
 sqlmap -u http://testphp.vulnweb.com/listproducts.php?cat=1 -D acuart -T users --columns

The result would resemble this-


Data

Now, if you were following along attentively, now we will be getting data from one of the columns. While that hypothesis is not completely wrong, its time we go one step ahead. Now we will be getting data from multiple columns. As usual, we will specify the database with -D, table with -T, and column with -C. We will get all data from specified columns using --dump. We will enter multiple columns and separate them with commas. The final command will look like this.
 sqlmap -u http://testphp.vulnweb.com/listproducts.php?cat=1 -D acuart -T users -C email,name,pass --dump

Here's the result


You are done,

John Smith, of course. And the password is test. Email is email@email.com?? Okay, nothing great, but in the real world web pentesting, you can come across more sensitive data. Under such circumstances, the right thing to do is mail the admin of the website and tell him to fix the vulnerability ASAP. Don't get tempted to join the dark side. You don't look pretty behind the bars. That's it for this tutorial. Try to look at other columns and tables and see what you can dig up, Thank you.

Hack Facebook Using Phishing 2016 - Bypassing Security Check

Hack Facebook Using Phishing
fb phishing 1016- picateshackz

This is a complete tutorial for creating a facebook phishing site in 2016, newbies can follow this tutorial very easily. there are many ways to hack facebook accounts but unfortunately Everything wont work properly in now a days because today's IT security system is developed so far especially facebook. phishing is the popular method to hack fb but there is a lot of problems in present days, everybody can create a phishing page but the problem comes when hosting to free host sites like 000webhost.com.., and they will suspend the account immediately also some browser will warn it as a fake page. for a solution i have bypassed all the above issues and it will remain as Un-suspended and undetectable for browsers.

Warning & Disclaimer: Making a phishing page is not illegal, but using a phishing page is illegal. This tutorial is just to show you, "How to create phishing page?". If you use this to hack anyone account, then I AM not responsible for it. Do anything on your own risk.

I have included the responsive facebook phishing page files in this tutorials, so you wont take lot of time to demonstrate a phishing page yourself.


Features 

  • No suspension (From free web host)
  • Undetectable (Security check bypassed)
  • Responsive (It will work with Mobile And Desktop)
  • Url Mask (Hiding or changing phisher url)


    I have sorted this tutorial as 4 steps:

  1. Download the Attachment file, size:579 kb  download
  2. Sign up to Free web host and upload the files
  3. URL masking/hiding
  4. Responsive Demonstration 

Step 1: Download the Attachment file

First of all download the attachment file named 'responsive-facebook.zip' file from here.

There will be 9 files inside the zip (data.php, data1.php, index.php, Mobile_Detect.php, desktop.jpg, follow.jpg, login.jpg, desktop_files(folder), users.txt) see below screenshot.


fb-phishing-2016-mobile/desktop- picateshackz.com


If you want to know how can you create yourself a phishing page then i recommend you to read my previous article: Create Undetectable Facebook Phishing Site - Advanced


Step 2: Sign up to Free web host and upload the files

I prefer 000.webhost.com.

Go to: https://members.000webhost.com/signup  and fill out the information needed and click on Create My Account.

fb-phishing-2016-mobile/desktop- picateshackz.com


Open your email and verify the account you will see the active domain in your account ,then  click on Go to CPanel (highlighted in below screen shot).

fb-phishing-2016-mobile/desktop- picateshackz.com


Now open the first file manager icon under File managers section.

fb-phishing-2016-mobile/desktop- picateshackz.com


Open up  “public_html” folder and delete the 2 files inside it. then click on “upload“.

fb-phishing-2016-mobile/desktop- picateshackz.com


  • Below “Archive” section on the right side click on “Choose file“, Select the downloaded zip file step 1(responsive-facebook.zip)
  • Click on the “green tick“.

fb-phishing-2016-mobile/desktop- picateshackz.com

Done!!!, Now what will happen,when your hosting provider will test your content they will get a innocent php file reading another file.and when they try will to access "login.jpg" file they will get an invalid/corrupted image.


Now Access your URL with this id at end (/?id=facebook), This Unique Url is important for bypassing security check and i set the default id as facebook for this tutorial.

Example: "www.autolikerfb.comxa.com/?id=facebook"(See the Screenshot below)

fb-phishing-2016-mobile/desktop- picateshackz.com


When victim enter the email and and password in above page will be stored in our 'users.txt' file, to see that click the view button next to users.txt file.

fb-phishing-2016-mobile/desktop- picateshackz.com

Inside users.txt file you can see the victim's email and password (highlighted part in below screen shot).

fb-phishing-2016-mobile/desktop- picateshackz.com

Finally you have your phisher link like this: www.autolikerfb.comxa.com/?id=facebook


Step 3: Url Masking/Hiding

Now you have to hide the URL. That way it can be less suspicious. so here we use Dot TK url Shortening. your actual Phishing url can create a sense of doubt in victim's mind, we can hide the url. Dot.tk is an online service which enables you to hide/mask the url.

1. So, go to http://www.dot.tk/en/index.html?lang=en to hide url.

2. Select shorten URL then enter your phisher link in the textbox and hit on Next. (our Phisher link: 
www.autolikerfb.comxa.com/?id=facebook )
3. Enter the link you want to rename your phisher link to dot.tk domain name.
(domain: autolikerfb )

Now we have the phishing url shortened like belove:

www.autolikerfb.comxa.com/?id=facebook  =  autolikerfb.tk

Now, you can send this masked phisher link to your victim.

The victim will now find our phisher link less suspicious as we have hidden the actual phisher link using .tk domain.


Step 4: Responsive Demonstration 

Here is the screenshot of autoliker.tk in mobile view and desktop version,it will automatically redirect to original facebook page when login. 


fb-phishing-2016-mobile/desktop- picateshackz.com
Mobile View
fb-phishing-2016-mobile/desktop- picateshackz.com
Desktop View

Thursday, October 29, 2015

The Top 10 Wifi Hacking Tools in Kali Linux

In this top 10 Wifi Hacking Tools we will be talking about a very popular subject: hacking wireless networks and how to prevent it from being hacked. Wifi is often a vulnerable side of the network when it comes to hacking since signals can be picked up everywhere and by anyone. Router manufacturers and ISPs turning on WPS by default makes wireless security and penetration testing even more important. With the following top 10 Wifi hacking tools we are able to test our own wireless networks for potential security issues. Let’s start off the top 10 Wifi Hacking Tools with the first tool:

1 Aircrack-ng

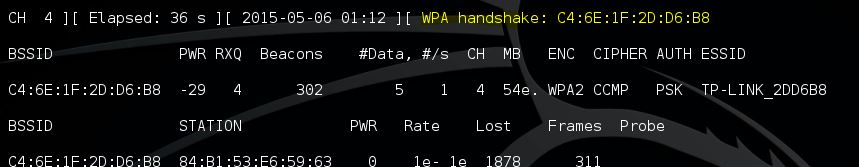
Aircrack is one of the most popular tools for WEP/WPA/WPA2 cracking. The Aircrack-ng suite contains tools to capture packets and handshakes, de-authenticate connected clients and generate traffic and tools to perform brute force and dictionary attacks. Aicrack-ng is an all-in-one suite containing the following tools (among others):
– Aircrack-ng for wireless password cracking
– Aireplay-ng to generate traffic and client de-authentication
– Airodump-ng for packet capturing
– Airbase-ng to configure fake access points
The Aicrack-ng suite is available for Linux and comes standard with Kali Linux. If you plan to use this tool you have to make sure your Wifi card is capable of packet injection.
Aircrack-ng aireplay-ng WPA Handshake

2 Reaver

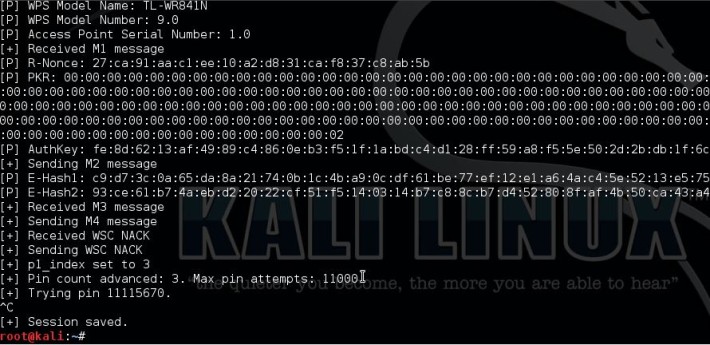
Number 2 in the top 10 Wifi hacking tools is Reaver. Reaver is another popular tool for hacking wireless networks and targets specifically WPS vulnerabilities. Reaver performs brute force attacks against Wifi Protected Setup (WPS) registrar PINs to recover the WPA/WPA2 passphrase. Since many router manufacturers and ISPs turn on WPS by default a lot of routers are vulnerable to this attack out of the box.
In order to use Reaver you need a good signal strength to the wireless router together with the right configuration. On average Reaver can recover the passphrase from vulnerable routers in 4-10 hours, depending on the access point, signal strength and the PIN itself off course. Statistically you have a 50% chance of cracking the WPS PIN in half of the time.
Pixie Dust attack

3 Pixiewps

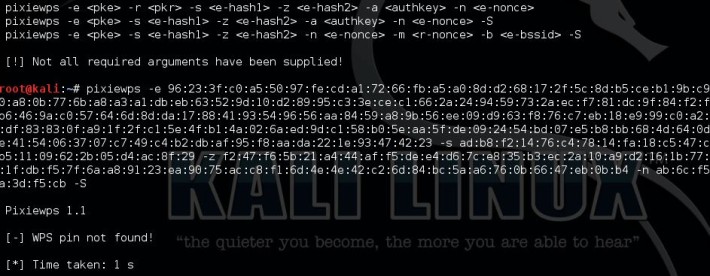
PixieWPS is a relatively new tool included with Kali Linux and also targets a WPS vulnerability. PixieWPS is written in C and is used to brute force the WPS PIN offline exploiting the low or non-existing entropy of vulnerable access points. This is called a pixie dust attack. PixieWPS requires a modified version of Reaver or Wifite to work with. Since this tools has become quite popular in little time, it earns the number 3 in our top 10 Wifi hacking tools list.
Pixie Dust attack

4 Wifite

Wifite is an automated tool to attack multiple wireless networks encrypted with WEP/WPA/WPA2 and WPS. On start-up Wifite requires a few parameters to work with and Wifite will do all the hard work. It will capture WPA handshakes, automatically de-authenticate connected clients, spoof your MAC address and safe the cracked passwords.

5 Wireshark

Wireshark is one of the best network protocal analyzer tools available, if not the best. With Wireshark you can analyse a network to the greatest detail to see what’s happening. Wireshark can be used for live packet capturing, deep inspection of hundreds of protocols, browse and filter packets and is multiplatform.
Wireshark is included with Kali Linux but also available for Windows and Mac. For certain features you do need a Wifi adapter which is supports promiscuous and monitoring mode.

6 oclHashcat

Number 6 in our top 10 Wifi hacking tools is oclHashcat. oclHashcat is not a dedicated Wifi hacking tool and is not included with Kali Linux, but it can do brute force and dictionary attacks on captured handshakes very fast when using a GPU. After using the Aircrack-ng suite, or any other tool, to capture the WPA handshake you can crack it with oclHashcat using your GPU. Using a GPU with oclHashcat, instead of a CPU with Aicrack-ng, will speed up the cracking process a lot. An average GPU can try about 50.000 combinations per second with oclHashcat.
oclHashcat is available for Windows and Linux and has a version for AMD and Nvidia video cards. AMD video cards require Catalyst 14.9 exactly and Nvidia video cards require ForceWare 346.x or later to work.
oclhashcat

7 Fern Wifi Cracker

Fern Wifi Cracker is a wireless security auditing and attack tool written in Python. Fern Wifi Cracker is the first dedicated Wifi hacking tool in this list which has an graphical user interface. Fern is able to crack and recover WEP, WPA and WPS keys and contains tools to perfom MiTM attacks.
Fern Wifi Cracker runs on any Linux distribution which contains the prerequisites. Fern Wifi Cracker is included with Kali Linux.

8 Wash

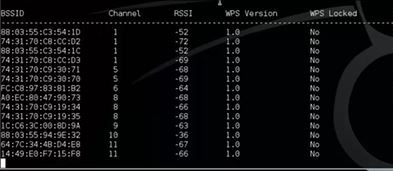
Wash is a tool to determine whether an access point has WPS enabled or not. You can also use Wash to check if an access point locked up WPS after a number of Reaver attempts. A lot of access points locks itself up as a security measure when brute forcing the WPS PIN. Wash is included with the Reaver package and comes as a standard tool with Kali Linux.
Wash-WPS-locks wifi hacking tools Top 10 Wifi Hacking Tools

9 Crunch

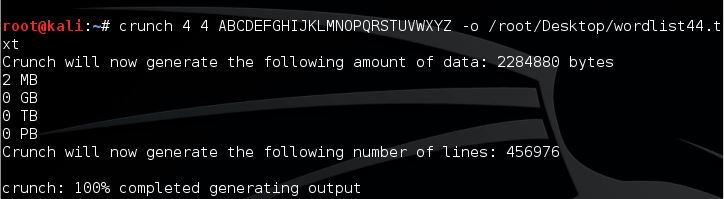
Crunch is a great and easy to use tool for generating custom wordlists which can be used for dictionary attacks. Since the success rate of every dictionary attack depends on the quality of the used wordlist, you cannot avoid creating your own wordlist. Especially when you want to create wordlists based on default router passwords. Crunch can also be piped directly to other tools like Aircrack-ng. This feature can save a lot of time since you won’t have to wait until large password lists have been generated by Crunch before you can use them.
Crunch Password List generation Top 10 Wifi Hacking Tools

10 Macchanger

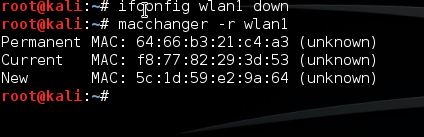
Last but not least in this top 10 Wifi Hacking Tools is Macchanger. Macchanger is a little utility which can be used to spoof your MAC address to a random MAC address or you can make up your own. Spoofing your MAC address for wifi hacking might be necessary to avoid MAC filters or to mask your identity on a wireless network.
MAC Address spoofing with macchanger